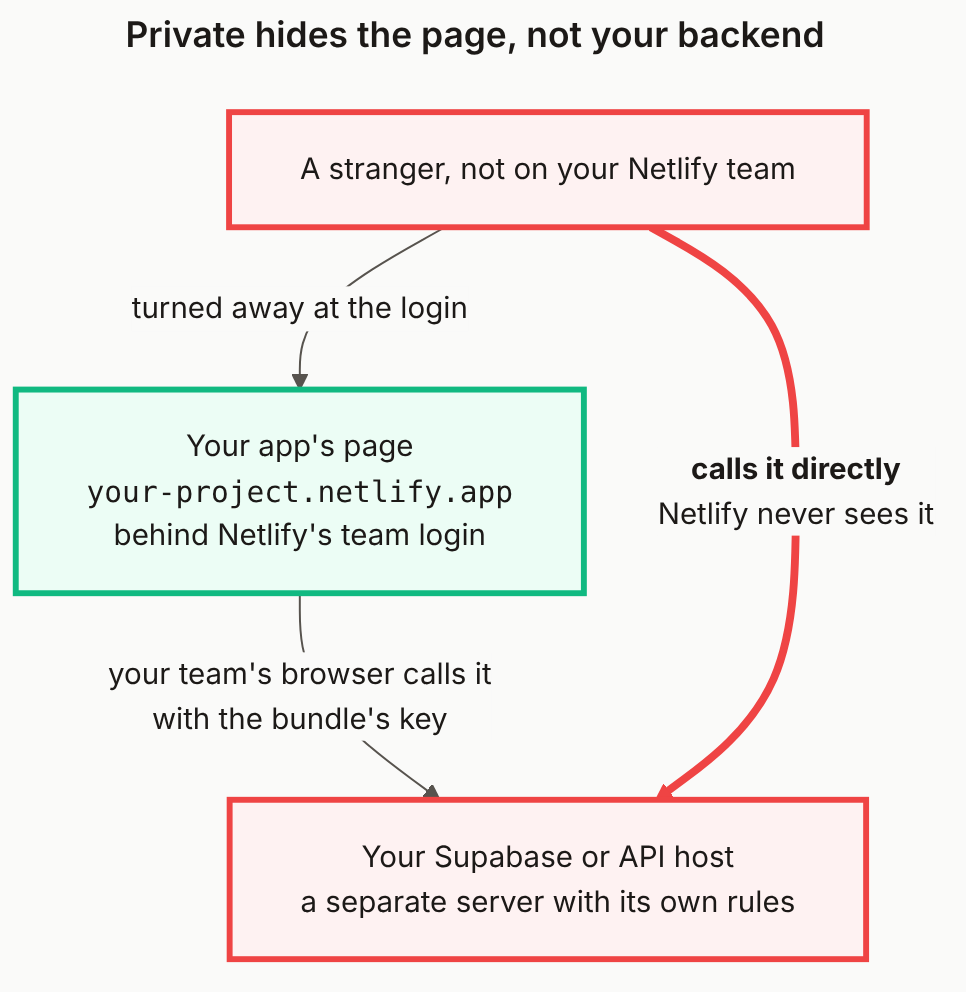
Netlify started making new projects private by default for new teams on July 28, 2026, and existing teams can switch it on themselves. It's a real lock. This diagram shows exactly which door it's on, and the one next to it that it leaves alone.
Reading the diagram
Top, red: a stranger. Red means someone who can reach things they shouldn't. They aren't on your Netlify team and have no login.
Left, green: your page, behind the login. When the project is private, Netlify checks for a team login before it serves anything at your-project.netlify.app. The stranger gets turned away there. That part works, and it's why the box is green.
Bottom, red: your backend. Your Supabase project, Firebase instance or API server lives on its own host. Your team's browser reaches it the normal way: the page loads, the JavaScript bundle reads the URL and the key compiled into it, and calls out. Netlify serves that bundle but plays no part in the call itself.
The thick red arrow is the point. The stranger doesn't need your page to make the same call. If they have the URL and the key, they send the request straight to the backend, and Netlify's visibility check never sees it happen. Whatever the backend allows an anonymous caller to do, the stranger can do.
That's why the backend box is red even though nothing about it is broken. Its colour isn't decided by Netlify. It's decided by its own rules: row level security on Supabase, an auth check on each API route.
What to do with it
Make the project private if it should be, then treat the backend as if the page were public anyway. Turn on row level security for every table the anon key can reach, check each API route for authentication, and rotate any key that was in the bundle while the project was public. The full walkthrough, including the webhook trap private visibility causes, is in Netlify Private Projects: What It Hides and Breaks.
The Mermaid source
Copy this and swap in your own backend.
---
title: "Private hides the page, not your backend"
---
flowchart TB
    A["A stranger, not on your Netlify team"]
    P["Your app's page<br/><code>your-project.netlify.app</code><br/>behind Netlify's team login"]
    D["Your Supabase or API host<br/>a separate server with its own rules"]

    A -->|"turned away at the login"| P
    P -->|"your team's browser calls it<br/>with the bundle's key"| D
    A ==>|"<b>calls it directly</b><br/>Netlify never sees it"| D

    classDef danger fill:#fef2f2,stroke:#ef4444,stroke-width:3px,color:#1c1917
    classDef safe fill:#ecfdf5,stroke:#10b981,stroke-width:3px,color:#1c1917

    class A,D danger
    class P safe

    linkStyle 2 stroke:#ef4444,stroke-width:4px
Does a private Netlify project protect my Supabase database?
No. Netlify's visibility setting puts a team login in front of the page at your netlify.app URL. Your Supabase project is a different host on a different domain, and Netlify never sees requests to it. Anyone with its URL and anon key can call it directly, so row level security is still what decides what they can read.
How would a stranger get my backend URL if the page is private?
The usual way is that the project was public before you made it private, and the bundle with the URL and key was loaded, cached or scraped then. Making it private later doesn't take that copy back.
What should I lock down besides Netlify visibility?
The backend's own access rules. On Supabase that means row level security on every table the anon key can reach. On your own API it means an authentication check on each route. Then rotate any key that was compiled into the bundle while the project was public.
Does private visibility hide my API keys?
It hides them from people who can't load the page. The keys are still compiled into the JavaScript bundle, so every team member can read them, and the day the project goes public again everyone can.
Is your backend open behind a private page?
A CheckYourVibe scan reads your deployed bundle and checks what the keys in it can actually reach.